Why Texans Live and Die by the Gun

posted in: All news | 0

The progun shibboleth that “The only thing that stops a bad guy with a gun is a good guy with a gun” has become so commonplace that it’s easy to forget its grisly origin. 

In 2012, after a 20-year-old with severe mental illness who was raised by a gun-loving mother killed 20 first graders at a Connecticut elementary school, National Rifle Association (NRA) President Wayne LaPierre made the phrase his opening salvo in what would become a successful campaign to derail national gun control legislation. Only “properly trained, armed good guys,” he claimed, stand between America’s vulnerable children and its “genuine monsters.” 

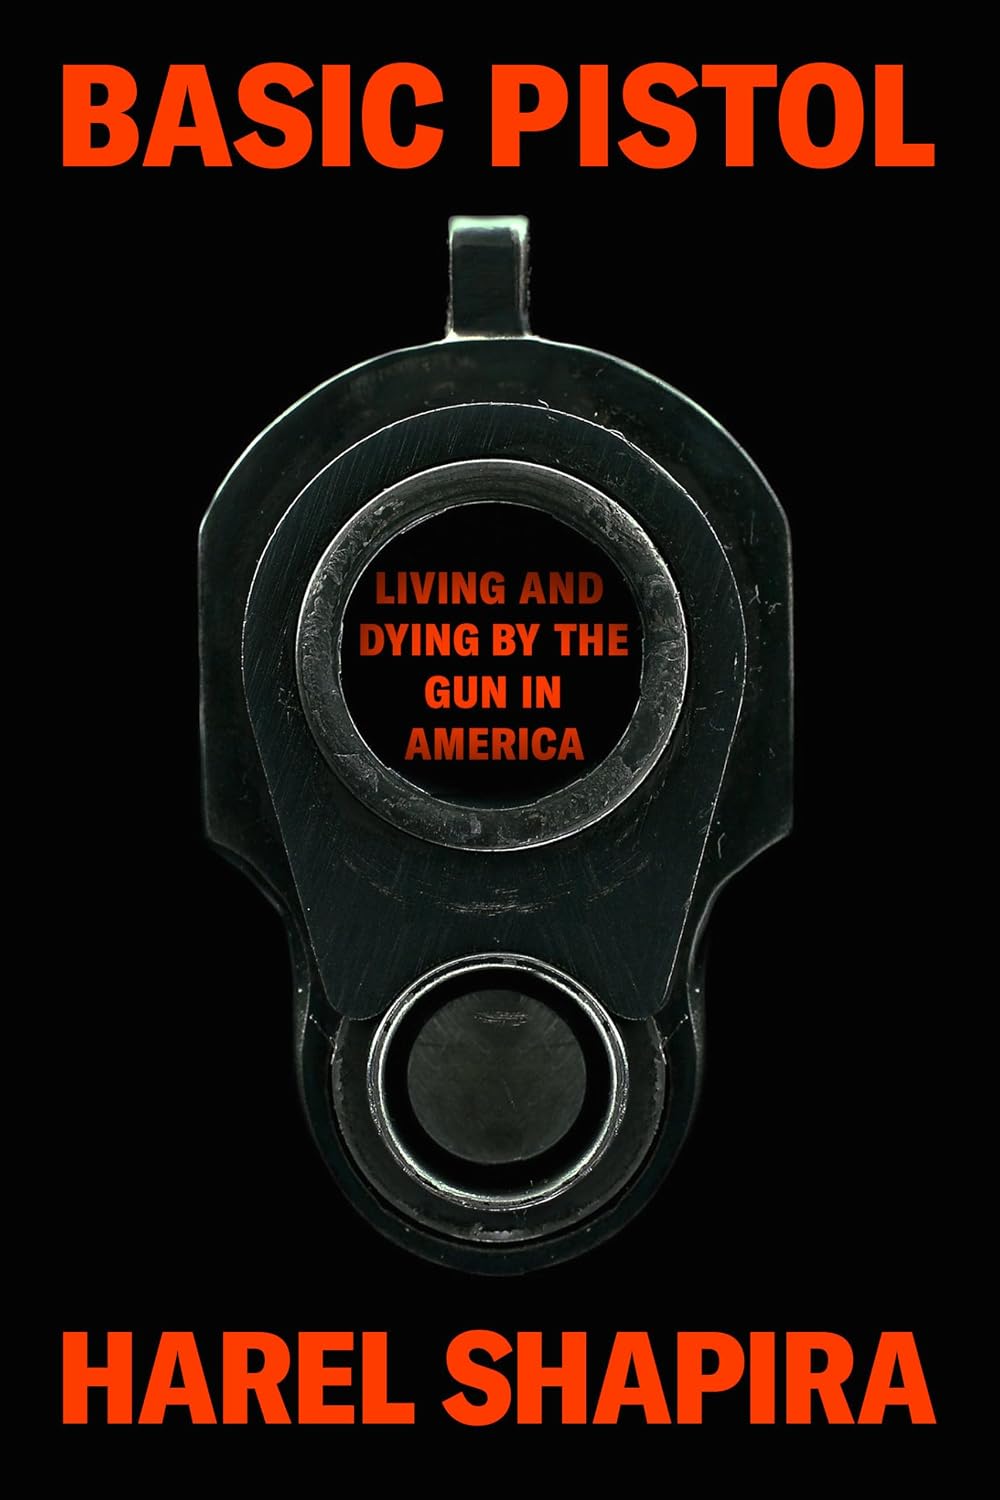
The year after Sandy Hook, sociologist Harel Shapira took an academic appointment at the University of Texas at Austin and began spending time where many of America’s gun-owning “good guys” are ostensibly being forged: the firearms training center. While his new book-length culmination of that research, Basic Pistol: Living and Dying by the Gun in America, briefly mentions the time he spent at schools in crunchy Portland, Oregon, and liberal suburban Massachusetts, the bulk of Shapira’s narrative unfolds in the rural middle of the Dallas-Houston-San Antonio triangle, where Shapira participated in a legion of courses at a center he pseudonymizes as “Tactical Training.” 

While Texas is often typecast as “the mythic heart of American gun culture,” Shapira argues that it is more bellwether than avant-garde. In 1995, under then-Governor George W. Bush, it became the 22nd state to pass a concealed carry law, which gave Texans the right to carry a handgun in public, provided they completed a training course. Firearms classes boomed and increasingly specialized in training citizens in armed self-defense, a once-rare rationale for gun-owning that would soon eclipse hunting or sport as the dominant justification. They became settings where Texans were inculcated not just with the rudiments of gun use but with a whole way of life.

“I guess you could call it a church,” Tactical Training’s main instructor admits to Shapira, while another teacher jokes that while his wife “carries a rosary … I carry a gun.” 

Basic Pistol: Living and Dying by the Gun in America

The comparison is apt. In this book, there are fire-and-brimstone preachers and enthusiastic converts. (Apostates are much rarer.) There is an agreed-upon catechism and points of dogmatic dispute, such as the NRA’s recommendation to always keep your gun unloaded, which Shapira’s instructor ignores, declaring that doing so is an undue burden. There is a sly mingling of faith and commerce, wherein the exhortation to believe tends to be followed by the injunction to open your wallet. There are patron saints and pilgrimages to holy sites, like the school of a famed instructor who brags about his former students who have been involved in self-defense shootings. Above all, there is an intensely felt moral Manichaeanism: The armed and virtuous elect must prepare to enact righteous violence against the evil perpetrators who seem to lurk around every corner. 

Tactical Training’s main instructor, whom Shapira pseudonymizes as “Tom Krone,” claims that self-defense is a natural evolutionary instinct, “something humans have been doing since the dawn of time.” But Shapira’s book clearly depicts how firearm training centers assiduously cultivate a hair-trigger sensibility. The good guy with a gun is made, not born, and he is made through fear. 

Basic Pistol is full of descriptions of macabre role-playing games, often requiring students to imagine how they might react to witnessing a loved one’s rape. An instructor says he even brought his own daughter to act in a scenario in which she is sexually assaulted. Tactical Training’s lessons also routinely foreground mentally disabled people, who are portrayed as “irrational forces of violence” incapable of feeling pain, giving the student with a gun no choice but to wield it. 

Shapira’s instructors claim to be cribbing their confected scenarios from real-life stories in the news. Their training, they argue, simply reflects the violent reality of a world where, as one instructor puts it, “evil is everywhere.” But Shapira punctures the pretensions of this hard-bitten realism. In one revealing example, the students are presented with a scenario in which a restaurant owner is closing up shop and comes across a deranged drunk person, who violently attacks. Shapira reads the corresponding newspaper clipping and learns that the owner had simply encountered a homeless man who’d come into the restaurant after it closed, looking for food and a bathroom. The exchange was completely nonviolent. In the dog-eat-dog world of Tactical Training, however, such an encounter with a stranger is no occasion for dialogue, let alone mercy. 

The result of this social conditioning is that many of Shapira’s fellow students live in what he calls “a never-ending loop of risk perception and reduction.” Workaday encounters with fellow citizens, such as eating at a restaurant or filling up on gas, become freighted with mortal peril. In one darkly comic scene, Shapira has a video call with an instructor who demonstrates how he keeps his gun at the ready while sitting on a public toilet. (It’s more complicated than you might think.) Shapira writes that his instructors wanted him to draw, aim, and fire so frequently—including by practicing at home without live ammo, like Travis Bickle in Taxi Driver—that it became “automatic, instinctual.” 

A few months into his time at Tactical Training, one of Shapira’s instructors confronts, in real life, the kind of scenario that firearm classes are designed for. Early one morning, a young Black man whom Shapira calls “Isaac” breaks down the front door of an instructor he calls “Michael.” After yelling at Isaac to leave, Michael shoots him five times, including once in the back, killing him. He refuses a request from his 911 dispatcher to check if Isaac is alive. “’Cause I am thinking, ‘Dude’s got friends,’” he tells Shapira. 

Isaac turns out not to be a burglar trailed by shadowy accomplices, but rather a young man suffering from severe mental disabilities who, seemingly in distress, had run out from a nearby home for people with special needs. He is the sort of person routinely dehumanized by Tactical Training’s instructors as both subhuman and superhuman, and, in the wake of the killing, the instructors vilify him in familiar terms. Krone calls him “a crazy person who doesn’t feel pain”; another describes him as “retard strong.” The police deem the shooting a justifiable homicide. 

Debates about gun violence, whether committed by private citizens or police, tend to narrow the aperture to the moment of the shooting alone, to focus on the question of what was in the gunman’s mind when he pulled the trigger: Did he fear for his life? Shapira deems such questions secondary. Isaac’s shooting was, he argues, “not a split-second decision but rather the outcome of a long process.” 

More important are the ways American gun culture has socialized millions of people to believe in the necessity of carrying machines designed to kill—and in the righteousness of using them against subjectively perceived threats. Michael himself articulates his pride at how “mechanically proficient” the killing was; he compares it to how, for an academic like Shapira, typing on a computer must become second nature. 

The gun control movement is animated by the tragedy of deaths like Isaac’s, and rightly so. But Basic Pistol also suggests a deeper tragedy wrought on the relationships of trust and mutuality that make American democracy possible in the first place. The gun lobby likes to claim that an “armed society is a polite society.” But Shapira’s sobering book reveals more of a Hobbesian war of all against all, one in which our neighbors appear as so many potential threats to our lives and liberty, rather than equal members of a shared democratic project. 

The post Why Texans Live and Die by the Gun appeared first on The Texas Observer.

Donna Sicuranza: Who She Is and Why Two Different Women Share the Name

posted in: All news | 0

Search “Donna Sicuranza” and the results don’t line up the way you’d expect for a single person. Some pages describe decades of nonprofit leadership in Connecticut animal welfare. Others describe a life spent in New York banking, a 1960 wedding, and a death in 2017. Read a few of these pages back to back and you’ll notice they’re clearly not describing the same woman — even though several articles blend the two together as if they were.

They’re not the same person. This happens more often than people expect with common first-and-last name combinations, and it’s worth untangling properly rather than assuming search engines got it right by default.

This piece focuses on verified, public information about the woman most people searching this name are actually looking for — a Connecticut nonprofit executive — while being upfront about where the second, unrelated woman fits into the picture, so you’re not left cross-referencing two life stories that don’t belong together.

The Donna Sicuranza Most People Are Searching For

The Donna Sicuranza with an active public profile today is a nonprofit executive associated with Tait’s Every Animal Matters (TEAM), a Connecticut-based animal welfare organization. TEAM’s own staff listing identifies her professionally as Donna Sicuranza Marconi, and she’s held the role of Executive Director since the organization’s founding.

What TEAM Actually Does

TEAM was established in 1997 to address a specific, practical problem: a growing population of unowned and under-cared-for cats across Connecticut, and limited affordable access to spay, neuter, and vaccination services for the people trying to manage it. Rather than building a traditional stationary clinic, the organization’s founders — including veterinarian Dr. John A. Caltabiano — put together a mobile surgical unit that could travel directly to communities.

Public information from the organization credits a bequest from animal advocate Vernon A. Tait with helping fund the initial mobile clinic effort, which is where the organization’s name comes from. Since its first outing in March 1997, TEAM’s mobile clinic model has been credited with providing services to more than 225,000 cats across Connecticut — a figure the organization has maintained and updated as its work has continued.

Donna Sicuranza’s Role

As Executive Director, her work centers on the administrative and operational backbone that keeps a mobile veterinary program running: staffing, scheduling, vehicle logistics, donor relationships, community partnerships, and compliance. It’s worth being precise here — she isn’t described anywhere in reliable sources as a veterinarian herself. The medical work (exams, surgery, vaccinations) is carried out by licensed veterinary staff, while her role has been about building and sustaining the organization that makes that work possible at scale.

Before her nonprofit career, available background describes experience in writing, editing, and public relations — a skill set that maps naturally onto the donor communication, community outreach, and public-facing work involved in running a nonprofit for close to three decades.

Quick Facts

DetailInformationFull professional nameDonna Sicuranza, publicly listed as Donna Sicuranza MarconiOrganizationTait’s Every Animal Matters (TEAM)RoleExecutive DirectorLocationWestbrook, ConnecticutOrganization founded1997Core programMobile feline spay/neuter/vaccination clinicReported impact225,000+ cats served since foundingBackgroundWriting, editing, and public relations prior to nonprofit leadership

The Other Donna Sicuranza — A Different Woman Entirely

Public obituary records document a separate woman, Donna Marie Sicuranza, who lived in Mt. Vernon and New Rochelle, New York, and passed away in March 2017 at age 74. According to her published obituary, she built a long career at the Bank of New York in Bronxville, married in 1960, and was remembered for decades of family life centered in the New York area, including time spent in Southampton.

There’s no documented connection between this woman and the Connecticut nonprofit executive — no shared employer, no shared organization, no overlapping timeline of public activity that ties the two together. They appear to simply share a first and last name, and automated content aggregation has a habit of merging distinct people who happen to share a name into a single, confused profile.

How to Tell Them Apart Quickly

Location: Connecticut (nonprofit executive) vs. New York (banking career, deceased 2017)

Field: Animal welfare nonprofit leadership vs. banking

Status: Actively listed in TEAM’s public staff directory vs. deceased since 2017

Public record type: Organizational biography and nonprofit press coverage vs. funeral home obituary

If the context you found the name in mentions cats, veterinary care, or Connecticut, you’re almost certainly looking at the nonprofit executive. If it mentions Bank of New York, Mt. Vernon, or a 2017 passing, that’s the other woman entirely.

You May Like: What Is Allysplay.com? The Real Gaming Blog Explained (2026)

Why So Much Online Content About This Name Is Unreliable

Worth flagging directly: several pages currently ranking for this name contain oddly phrased, factually garbled passages that read like unedited machine-generated text — sentences that trail off, invented emotional language with no clear source, and details that don’t track logically from one paragraph to the next. That’s a useful signal in itself. When researching a real person’s biography, especially someone without a large, well-documented public media footprint, cross-checking against an organization’s own staff page or a verifiable local news source is a better bet than trusting the highest-ranking result by default.

Frequently Asked Questions

Who is Donna Sicuranza?

The Donna Sicuranza most commonly referenced today is the Executive Director of Tait’s Every Animal Matters (TEAM), a Connecticut nonprofit running a mobile feline spay, neuter, and vaccination clinic since 1997. She’s also publicly listed as Donna Sicuranza Marconi.

Is Donna Sicuranza a veterinarian?

No. She leads the organization’s administration, planning, and fundraising. Licensed veterinary staff carry out all medical procedures at TEAM’s mobile clinics.

What is Tait’s Every Animal Matters (TEAM)?

TEAM is a Connecticut-based nonprofit founded in 1997 that operates a mobile clinic providing affordable spay, neuter, and vaccination services for cats, aimed at reducing feline overpopulation.

Are there two different people named Donna Sicuranza?

Yes. In addition to the Connecticut nonprofit executive, public obituary records document a separate woman, Donna Marie Sicuranza, who had a banking career in New York and passed away in 2017. The two aren’t connected.

How many cats has TEAM helped?

Public information from the organization credits its mobile clinic program with providing services to more than 225,000 cats since it began operating in 1997.

Why do search results about Donna Sicuranza seem inconsistent?

Because two unrelated people share the name, and some published content blends details from both without distinguishing them. Cross-checking against TEAM’s own staff listing is the most reliable way to confirm which Donna Sicuranza a source is actually describing.

Read More: Gessolini: Why Every Website Gives You a Different Answer (And What’s Actually True)

Cyberpsc.com Explained: What This Company Actually Does

posted in: All news | 0

If you searched “cyberpsc.com” expecting a cybersecurity company, you’re not the only one. The word “cyber” sitting right in the domain name practically begs that assumption, and at least one site currently publishing content about cyberpsc.com runs with exactly that guess — describing it as a “platform” for cybersecurity education and digital safety awareness.

That description doesn’t hold up.

Cyberpsc.com belongs to a general contracting company, and it has nothing to do with cybersecurity software, threat monitoring, or digital safety education. This is a good example of how a domain name alone can send both readers and low-effort content sites in completely the wrong direction — so let’s sort out what’s actually true.

Who’s Actually Behind Cyberpsc.com

Cyberpsc.com is the website of Cyber Professional Solutions Corp., a general contractor based in Southern California. According to the company’s own LinkedIn profile, the business specializes in construction and electrical low-voltage services, and has operated in the region since 2002.

A few verifiable specifics, drawn from business data listings and the company’s own public profile:

Headquarters: Chula Vista, California

Founded: 2002

Industry: Construction, with a focus on electrical low-voltage systems

Client base: Commercial, institutional, and government sector projects

Company size: A small, specialized team — public business records list it around seven employees

The company positions itself around long-term client relationships and project delivery, describing close collaboration with subcontractors and a focus on safety and quality control compliance across its projects. That’s a fairly typical profile for a specialty electrical/low-voltage contractor that’s built a reputation through repeat government and commercial work rather than public marketing.

What “Electrical Low Voltage” Actually Covers

For anyone unfamiliar with the term, low-voltage electrical work sits outside standard high-voltage power wiring and typically includes:

Structured cabling and network infrastructure

Security and access control systems

Fire alarm and life-safety systems

Audio-visual and communication system wiring

Building automation and control wiring

This is a specialized, licensed trade — and it’s a completely different discipline from cybersecurity, even though both fields get lumped under “technology” in casual conversation.

Where the “Cyber” Confusion Comes From

The word “cyber” has been attached to security and technology topics so consistently over the past two decades that almost any business using it in its name gets assumed into that category by default. That assumption isn’t unreasonable on its face — it’s just wrong here.

There’s a second layer of naming coincidence worth mentioning. In cybersecurity industry circles, “PSC” is sometimes used as shorthand for “private security contractor,” discussed in contrast to “PMC” (private military company) when people debate how to categorize firms doing offensive or defensive cyber work for governments and corporations. That’s a real term used in security industry commentary — but it’s an entirely separate concept from this company’s name, where “PSC” stands for the company’s own corporate name, Professional Solutions Corp. The overlap is coincidental, not connected.

Quick Comparison: Assumption vs. Reality

What People AssumeWhat’s Actually TrueA cybersecurity software companyA general contracting and electrical construction firmA digital safety education platformNo blog, courses, or awareness content published by the companyA tech startupOperating since 2002 in a traditional construction tradeAn online-only businessPhysical headquarters in Chula Vista, California, with on-site project workRelated to “cyber private security contractor” terminologyCoincidental naming overlap only — unrelated industries

Why This Matters Beyond Just Curiosity

This kind of mismatch isn’t just a fun trivia point — it has real consequences for anyone doing due diligence.

If you’re a government agency, general contractor, or business owner checking out cyberpsc.com because the company submitted a bid, appeared in a subcontractor list, or sent you a business email from a @cyberpsc.com address, you need accurate information, not a copy-pasted guess based on the domain’s name. Getting this wrong could mean:

Misclassifying a vendor during procurement or vetting

Confusing correspondence from this contractor with an unrelated cybersecurity vendor

Drawing the wrong conclusions in a background check or compliance review

That’s exactly the kind of situation where a single inaccurate article — especially one confidently describing a construction company as a “cyber technology platform” — can cause real friction for someone trying to verify a legitimate business contact.

You May Like: Gessolini: Why Every Website Gives You a Different Answer (And What’s Actually True)

How to Verify a Business Like This Yourself

Whether it’s Cyber Professional Solutions Corp. or any other lesser-known company you’ve come across, the same basic verification steps apply:

Check the company’s own LinkedIn or business profile, not just search snippets or generic content sites, for industry classification, headcount, and history.

Cross-reference business data providers (like LeadIQ, ZoomInfo, or state business registries) for headquarters address, incorporation date, and leadership names.

Confirm licensing where relevant — contractors, especially those doing electrical work, are typically required to hold state contractor licenses, which are publicly searchable through state licensing boards.

Be skeptical of vague, generic descriptions. A legitimate company profile includes specific, checkable details — an address, a founding year, named services. Content that describes a business only in broad, interchangeable language (“helps users stay informed in an increasingly connected world”) is a sign the writer didn’t actually verify anything.

Frequently Asked Questions

What is cyberpsc.com?

It’s the website of Cyber Professional Solutions Corp., a general contracting company based in Chula Vista, California, specializing in construction and electrical low-voltage services since 2002.

Is cyberpsc.com a cybersecurity company?

No. Despite the word “cyber” in the name, the business is a construction and electrical contractor, not a cybersecurity firm, and doesn’t publish cybersecurity content or offer digital security services.

What does Cyber Professional Solutions Corp. actually do?

The company handles construction and electrical low-voltage work, including structured cabling, security and access systems, and related infrastructure, for commercial, institutional, and government clients across Southern California.

Why do some websites describe cyberpsc.com as a cybersecurity platform?

That description appears to come from assuming the site’s focus based on the word “cyber” in the domain name, rather than verifying what the actual company does. It’s an inaccurate characterization not supported by the company’s own business profile.

Is cyberpsc.com a legitimate business?

Yes — public business data sources, including LinkedIn and B2B contact databases, confirm it as an active, established general contracting company with a specific location, founding date, and employee base.

Does “PSC” in the name relate to cybersecurity’s “private security contractor” term?

No, that’s a coincidental overlap. In this company’s name, PSC stands for Professional Solutions Corp., unrelated to the cybersecurity industry’s separate use of “PSC” as shorthand for private security contractor.

Read More: Incfidelibus: The Real Latin Story, the Scam History, and Why the Two Keep Getting Mixed Up

Incfidelibus: The Real Latin Story, the Scam History, and Why the Two Keep Getting Mixed Up

posted in: All news | 0

Most confusing search terms get confusing for one reason. This one gets confusing for two, and they have nothing to do with each other.

Reason one: “Incfidelibus” looks like Latin, and it’s close enough to a real Latin word that people assume it must mean something specific and old.

Reason two: the name “IncFidelibus” has a documented history online tied to ads for phone-monitoring and “hack a cheating partner’s phone” services — the kind of offer that shows up in comment sections and shady blog posts aimed at people going through a relationship crisis.

Neither of those two stories is fake, exactly. But treating them as one story — as several “complete guide” articles online currently do — creates a genuinely misleading picture. Let’s take them apart properly.

The Real Latin Behind the Word

Start with the language, because this part is actually verifiable.

There’s no standard classical Latin word spelled incfidelibus. Drop the extra “c,” though, and you land on infidelibus — a real, documented Latin form.

Infidelibus is the dative/ablative plural of infidelis, a Latin adjective built from in- (not) and fidelis (faithful), which itself comes from fides (faith, trust).

Standard Latin dictionaries define infidelis along the lines of “unfaithful,” “faithless,” or “not to be trusted.”

As a third-declension adjective, infidelis takes the ending -ibus in its dative and ablative plural forms — which is exactly where infidelibus comes from grammatically.

This form shows up in medieval Latin religious and theological writing, often in discussions about people outside a particular faith community.

So infidelibus is genuine. Incfidelibus, with the added “c,” isn’t an attested classical form. The most reasonable explanations are a spelling variant, an OCR or transcription error somewhere in digitized text, or simply a modern misspelling that picked up momentum online. None of that makes it an ancient hidden philosophy about loyalty and betrayal, despite what a few pages now claim — those interpretations are built on the look of the word, not on any documented source using it that way.

Quick Reference: Infidelis Family of Words

TermWhat It IsVerified?fidesLatin noun for faith/trustYes — core classical vocabularyfidelisLatin adjective, “faithful”YesinfidelisLatin adjective, “unfaithful/faithless”YesinfidelibusDative/ablative plural of infidelisYes — documented Latin grammatical formincfidelibus—No — not an attested classical Latin word

The Other History: A Name Tied to Hack-for-Hire Marketing

This is the part worth taking seriously, because it isn’t just trivia — it touches on real scams and real risk.

Separately from any Latin connection, “IncFidelibus” has shown up online as a brand name attached to posts and pages advertising phone-monitoring, WhatsApp access, and “catch a cheating partner” services. This style of marketing follows a familiar and well-documented pattern seen across dozens of similarly named operations:

Ads promise remote access to someone else’s phone — messages, call logs, location, sometimes even encrypted app content — without the target’s knowledge.

The pitch is almost always aimed at emotionally charged situations: suspected infidelity, custody disputes, monitoring an employee, or “catching” someone in a lie.

Contact usually happens through informal channels rather than a verifiable, established business.

Here’s the important context: services marketed this way fall into a category regulators and cybersecurity researchers refer to as stalkerware — software or “services” built to monitor a device without the device owner’s informed consent. That’s not a gray area. Installing monitoring software on someone else’s phone without their knowledge or consent is illegal in most jurisdictions, and it’s treated as a serious privacy and safety issue, particularly in the context of domestic abuse and relationship control.

There’s also a practical problem with the promise itself. Apps like WhatsApp, Signal, and iMessage use end-to-end encryption, which means messages can’t simply be intercepted mid-transit by a third party who doesn’t have physical or credential access to the actual device. Genuine access typically requires the target’s phone to already be compromised — through a previously installed app, a phished password, or physical access — not some kind of remote back door that any anonymous “hacker for hire” can flip on for a fee. That gap between the marketing promise and what’s technically realistic is exactly why this category of offer is so strongly associated with scams: payment upfront, fabricated “proof” screenshots, and no actual delivery.

You May Like: What Is Allysplay.com? The Real Gaming Blog Explained (2026)

If You’ve Seen “Incfidelibus” Associated With This Kind of Offer

Don’t send payment or personal information to an unverified “hacking” service. This is one of the most common relationship-crisis scam categories reported to consumer protection bodies.

Assume claims of secretly accessing someone’s WhatsApp or phone remotely, without their device, are wildly overstated at best.

If your concern is genuine — a partner you suspect of infidelity, or a safety concern involving a family member — the legitimate paths are relationship counseling, a licensed private investigator (where legally permitted), or law enforcement if there’s an actual crime involved, not an anonymous online “hacker.”

If your concern runs the other way — you think you’re being monitored without consent — that’s a stalkerware situation, and organizations like the Coalition Against Stalkerware and the National Network to End Domestic Violence publish guidance specifically for that.

What About Incfidelibus.com Today?

Search results indicate an active incfidelibus.com site as of 2026, and its current content reads as general informational and technology publishing rather than anything resembling the older phone-monitoring marketing associated with the name. That’s worth noting clearly: a domain’s current content and its historical branding are two different things, and one doesn’t necessarily reflect the other. If you land on a site using this name now, evaluate what’s actually on the page in front of you rather than assuming it connects to either the Latin curiosity or the older scam-adjacent history.

Why the Two Stories Keep Getting Blended Together

A handful of recent articles about this keyword present it as one continuous story: an “ancient Latin concept” tied to “themes of loyalty, trust, and betrayal” that somehow evolved into modern digital use. That framing is doing a lot of work to make two unrelated things sound like one elegant narrative.

In reality:

A real Latin word (infidelis) exists and genuinely relates to concepts of faithfulness and betrayal.

A misspelled variant of that word (incfidelibus) picked up separate, unrelated use as a brand name for phone-monitoring marketing — likely because the “unfaithful” theme fit the target audience (suspicious partners) a little too conveniently.

Later content, written to rank for the resulting search term, retrofit a “philosophical concept” narrative that connects the two, without documentation to support it.

Recognizing that chain is the actual answer to “what does incfidelibus mean” — not a single tidy definition, but an accurate account of how a coincidental resemblance between a scam brand name and a real Latin root turned into an entire wave of speculative content.

Frequently Asked Questions

What does incfidelibus mean?

There’s no standard classical Latin word spelled this way. It closely resembles infidelibus, the real dative/ablative plural form of infidelis (“unfaithful” or “faithless”). The extra “c” isn’t part of any documented classical form.

Is incfidelibus a real Latin word?

No — infidelibus (without the “c”) is the real, attested Latin form. Incfidelibus appears to be a spelling variant, likely a typo, OCR error, or modern misspelling.

Is IncFidelibus a hacking service?

The name has a documented history in online marketing for phone-monitoring and “catch a cheating partner” style services — a category widely associated with scams and stalkerware. Whether any specific current site using the name is connected to that history should be judged by what’s actually on the page today, not assumed either way.

Can someone really hack WhatsApp remotely through a service like this?

Legitimate cybersecurity understanding says this is highly unlikely as advertised. End-to-end encrypted apps generally require access to the actual device to retrieve message content, not a remote service with no access to the phone.

Is it illegal to monitor someone’s phone without their consent?

In most places, yes — installing monitoring software on someone else’s device without their knowledge and consent is illegal and falls under stalkerware and unauthorized computer access laws, separate from any parental-control use case that’s disclosed to the device owner.

Where does the “loyalty and betrayal philosophy” explanation of incfidelibus come from?

It appears to be a retroactive narrative built by content written to rank for this search term, connecting the real Latin meaning of “unfaithful” to the unrelated scam-marketing history under the same name. There’s no independent documentation supporting it as an established concept.

Read More: Gessolini: Why Every Website Gives You a Different Answer (And What’s Actually True)